
The short version
What you need to know.
- ASUS identifies the 3.0.0.6_102 firmware series but does not give an exact affected-model or fixed-build table in the sources checked.
- CVE-2026-93489 describes an unauthenticated adjacent-network attacker gaining administrator capabilities, not an internet-wide attack claim.
- Record your exact model and installed firmware, then check ASUS support. Routine updating is separate from confirmation of a CVE-specific fix.
What ASUS has confirmed
Your router probably gets less attention than the phone connected to it. Fair enough, until a security update needs doing. ASUS has published a bulletin covering router firmware, and one of the issues deserves a proper look before the next household internet maintenance session.
The ASUS-authored CVE-2026-93489 record, published on 23 October, describes an authentication flaw. A nearby attacker without a login could forge an access ticket and perform administrator operations. ASUS rates it High, with a CVSS 4.0 score of 8.7.
That score describes severity, not the chance your particular router has been compromised. The recorded attack vector is adjacent-network access. It does not establish that someone anywhere on the internet can use this particular flaw against your home connection. I have not tested the vulnerability or a firmware fix.
What the firmware family tells you
Both the ASUS security advisory and its CVE record identify the affected firmware family as `3.0.0.6_102 series`. They do not provide a model-by-model list or a specific fixed build for CVE-2026-93489 in the official material checked on 25 October 2026.
That is not enough to declare every ASUS router affected. It also does not let me give you a reliable version number and say, “install this and you are covered”. A firmware family is a starting point for checking, rather than a complete patch checklist.
My view is straightforward: owners deserve a clear model and version table. Until that is verified, a newer download should not be presented here as a confirmed fix for this CVE just because its number looks reassuring.
Check the exact router, then its firmware
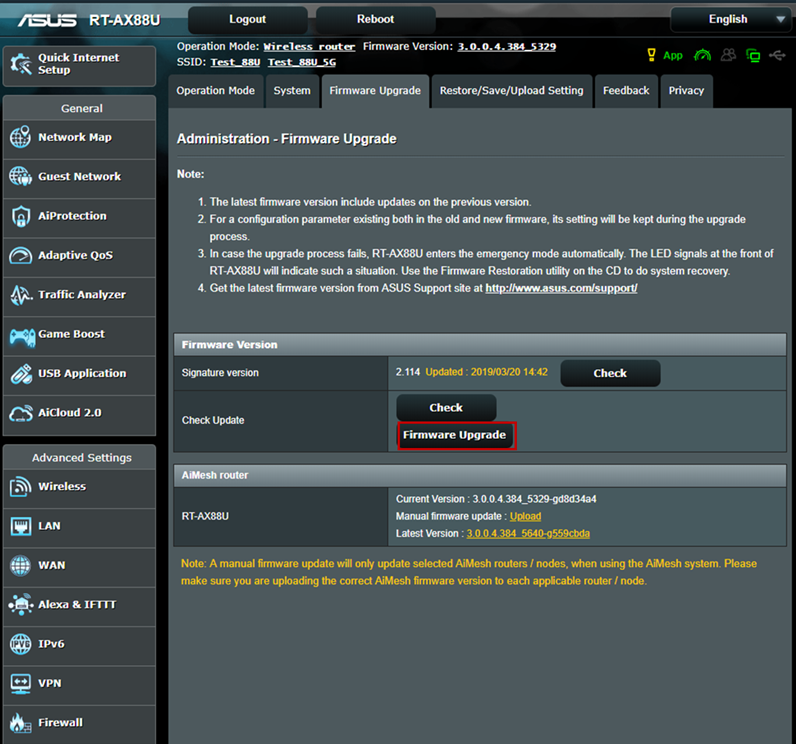
Start by recording your exact model and installed firmware version from the router administration interface. ASUS’s support guide shows these details in the interface header. Keep the full model name, including suffixes. Similar-looking product names are not permission to install another model’s firmware.
Use ASUS Support to find that model’s firmware downloads and release notes. Compare those with the installed build, looking for an explicit security advisory or fix reference. If the connection between the download and this CVE is unclear, ask ASUS support for the affected and fixed versions for your model.
ASUS’s official update guide covers the app and browser-based routes. For the browser interface, look under Administration and Firmware Upgrade. Follow the instructions for your model, allow for an interruption and keep power connected during the update. Schedule it around the household, because nobody enjoys a surprise reboot halfway through a work call.
Prepare before pressing update
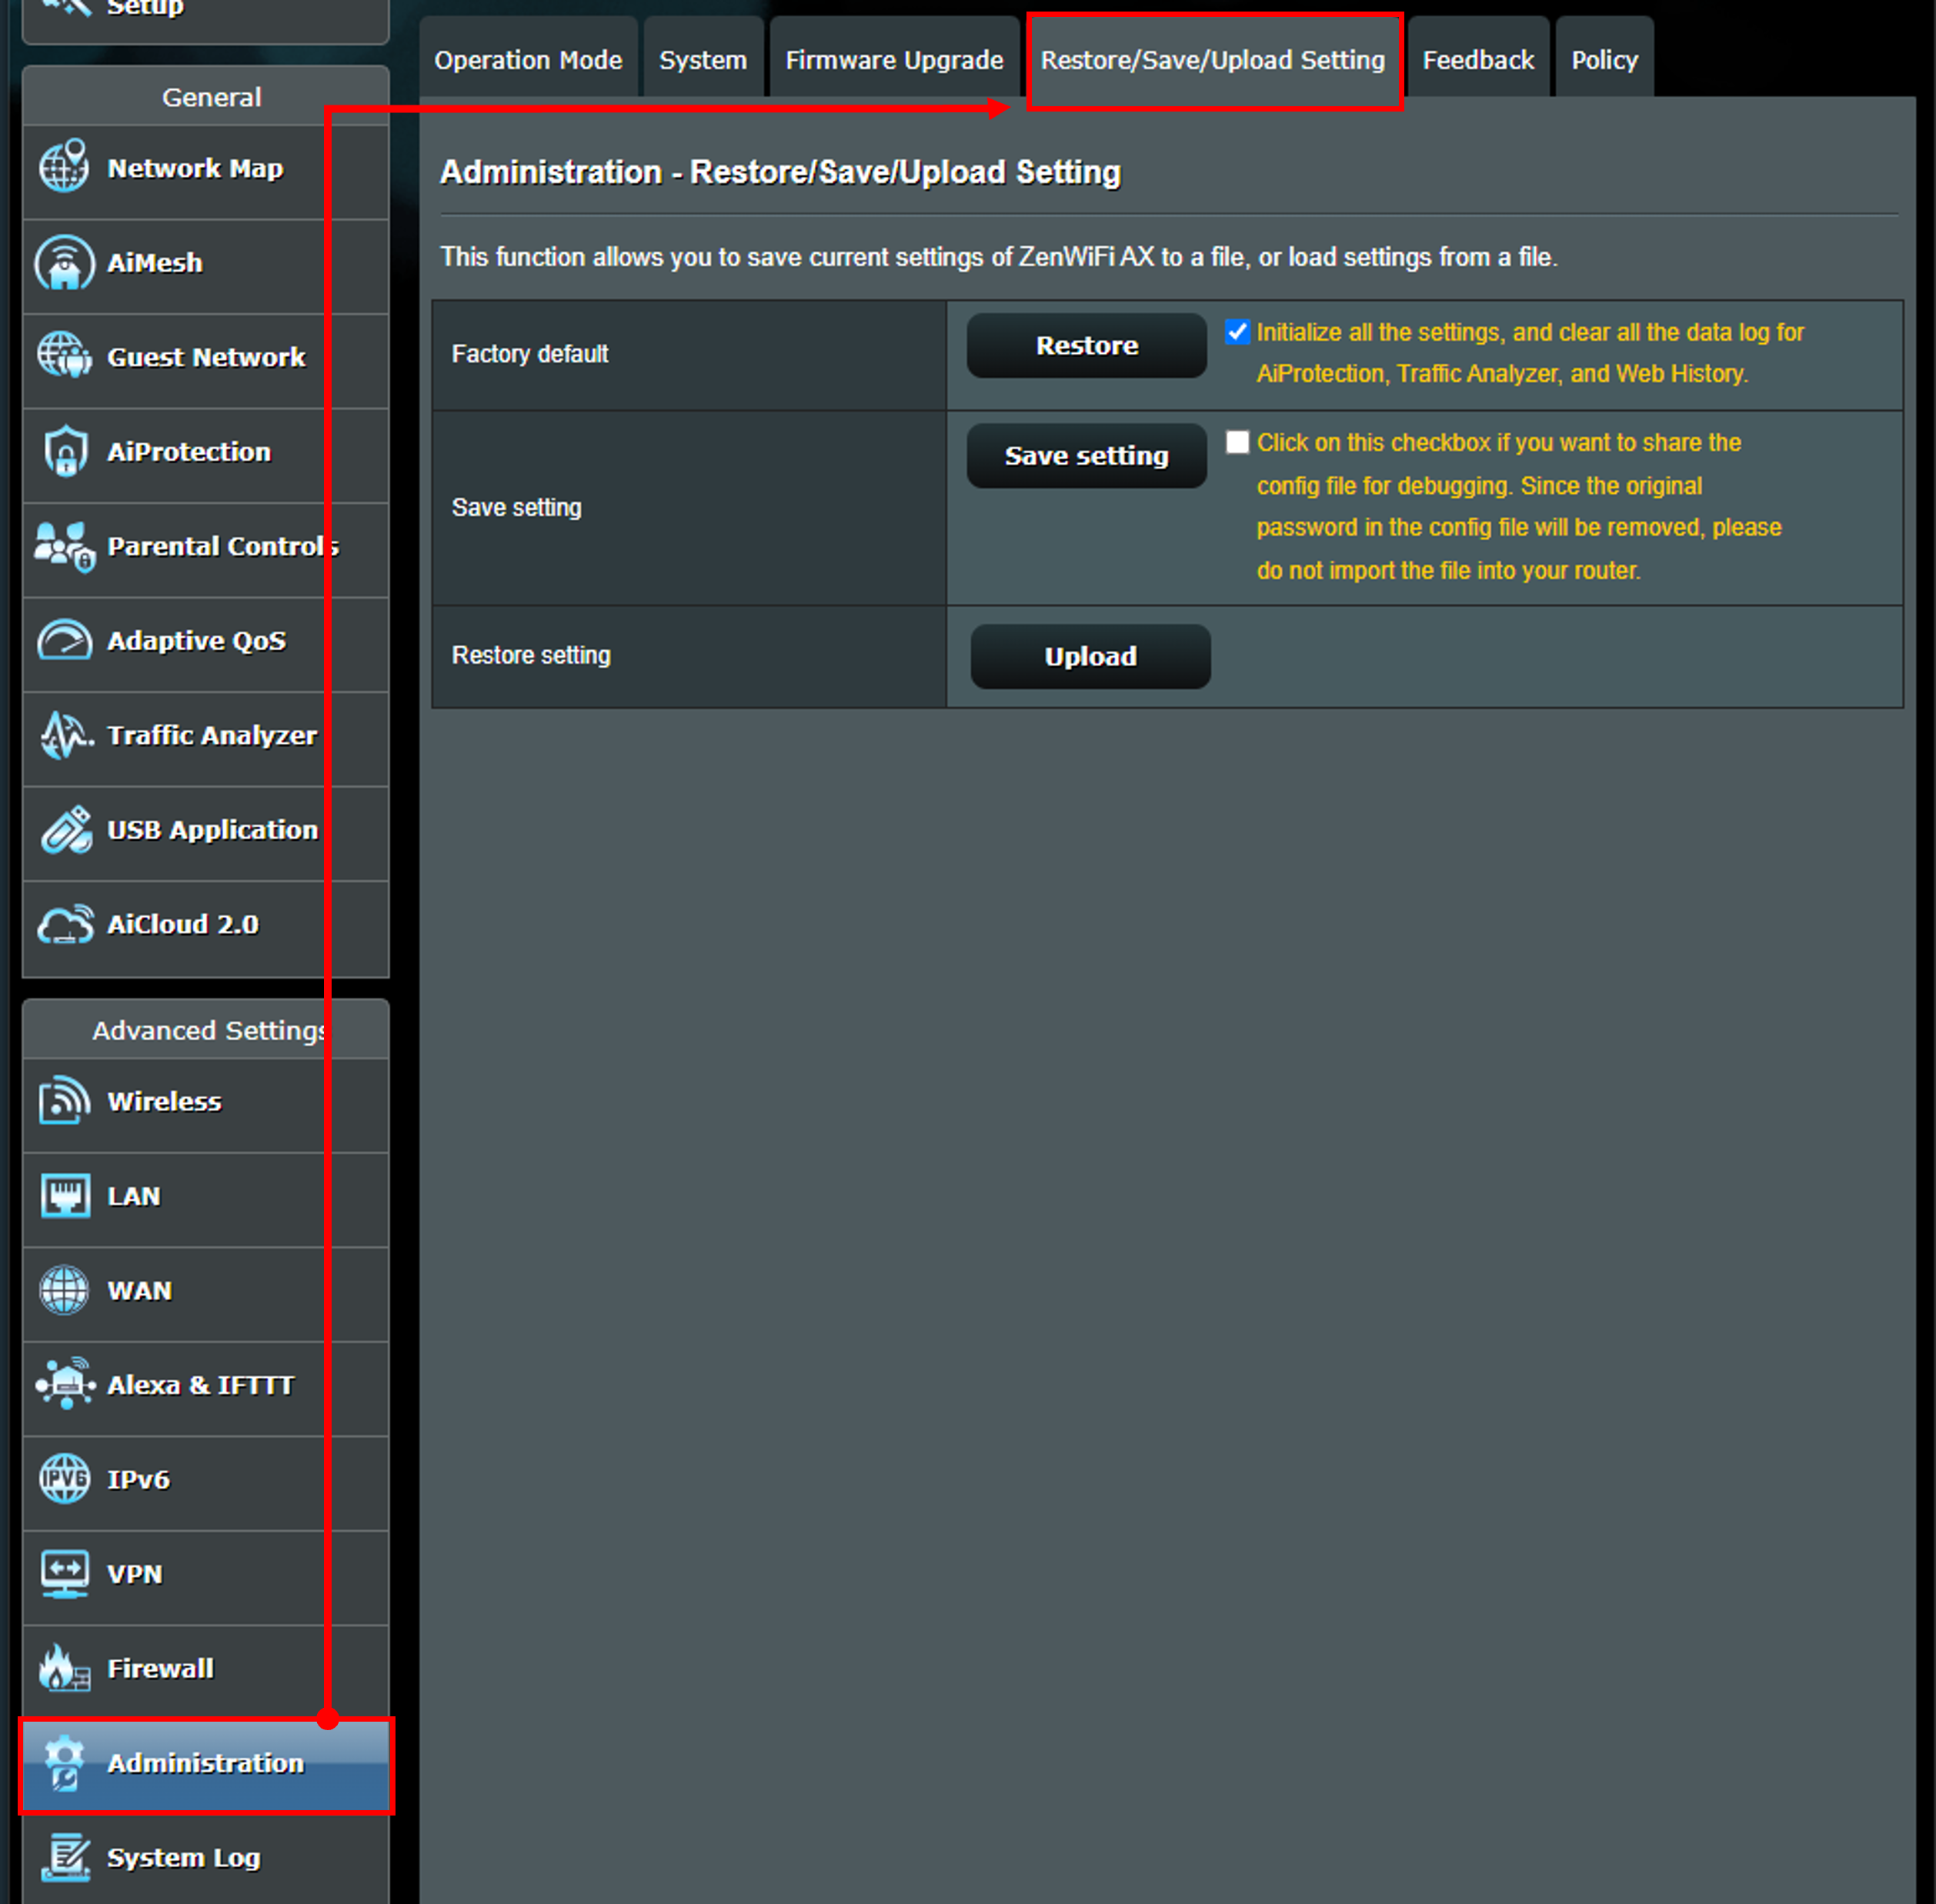
Save your settings using ASUS’s backup instructions and have the details needed to set up your connection again. Read the update procedure first, including any reset or reconfiguration instructions. A backup is useful preparation, not a reason to skip those steps.
If you cannot update immediately, ASUS advises restricting management to trusted local networks, disabling WAN management, keeping untrusted devices off the network and reviewing unfamiliar linked devices or companion-app sessions. Those precautions reduce exposure; they are not proof that this vulnerability has been removed. Strong passwords remain sensible, but a flaw that bypasses authentication cannot be dismissed because your password is good.
My practical advice is to check your router now and follow the manufacturer’s supported maintenance process. That is routine security housekeeping, not a promise that an available download fixes this CVE. If ASUS publishes a model and fixed-version table, that is the detail to compare against your own router.
Primary sources
Read the evidence.
- ASUS security advisory: Security Update for ASUS Router FirmwareASUS ↗
- ASUS-authored CVE-2026-93489: published 23 October 2026ASUS / CVE Program ↗
- Official firmware update instructionsASUS Australia ↗
- Official configuration backup instructionsASUS Australia ↗
Primary sources checked on 25 October 2026. Exact affected models and a CVE-specific fixed build were not supplied by the advisory or CVE record checked. This is document-based reporting; no vulnerability or patch was tested by Compare.
Community
Add to the article.
Useful experiences, questions and corrections make the next reader’s decision easier.
Comments appear here after moderation.